Measuring the robustness of an IT system means looking beyond intrusion prevention alone. RISC, an acronym for Networks, Computing, Trusted Systems, refers to a research approach that brings together software security, hardware security and trust models to assess a system’s ability to keep operating under degraded conditions. The focus has shifted: the goal is no longer simply to block an attack, but to quantify how well a system withstands, recovers from and adapts to an incident.
Digital dependencies and attack surface: what traditional audits fail to measure
Traditional audit methodologies assess security within a defined perimeter: servers, workstations and firewalls. RISC broadens this perspective by treating dependencies between networks, services and providers as a resilience factor. A system may be perfectly configured internally yet remain vulnerable through a third-party provider or a poorly isolated API.
In its Threat Landscape 2026, based on an analysis of incidents observed in 2025, ENISA highlights how these digital dependencies expand the attack surface and make both incident prevention and mitigation more difficult. The RISC approach addresses this dimension directly by modelling interactions between distributed components, whereas a one-off audit captures only a static snapshot.
Specialist organisations document these challenges and offer support frameworks; details of their services are available at https://www.risc.lu/, which covers several aspects of IT security and resilience.
Software security, hardware security and trust: comparing the three pillars of RISC
What makes RISC distinctive is its simultaneous treatment of three layers that most frameworks address separately. The table below compares these pillars against operational criteria.
| RISC pillar | Scope | Threats addressed | Example mechanism |
|---|---|---|---|
| Software security | Application code, libraries, updates | Unpatched vulnerabilities, injections | Static code analysis, automated fuzzing |
| Hardware security | Processors, firmware, side channels | Physical attacks, microarchitectural exploitation | Secure enclaves, boot integrity verification |
| Trusted systems | Distributed protocols, certification chains | Node compromise, identity forgery | Byzantine fault-tolerant consensus algorithms |
A system that addresses only the software layer remains exposed to hardware side-channel attacks. Conversely, secure hardware is of little use if the software running on it contains known vulnerabilities. Resilience comes from the convergence of all three layers, not excellence in just one.
IT resilience against long-standing vulnerabilities: the role of RISC research
Some recent incidents have exploited vulnerabilities that have been documented for years. Research teams working within the RISC approach, such as those at LAAS-CNRS, study the modelling of critical systems and how faults propagate through distributed architectures.
Their work focuses in particular on:
- Network virtualisation and softwarisation, which introduce new attack surfaces with each added layer of abstraction
- Artificial intelligence for anomaly detection, with a focus on frugality to prevent the defence mechanism itself from becoming a source of complexity
- Fault-tolerant distributed algorithms, which allow a system to keep operating even when one or more of its components are compromised
This last point distinguishes resilience from security alone. A resilient system does not prevent every compromise; it limits its spread and maintains a degraded but functional service.
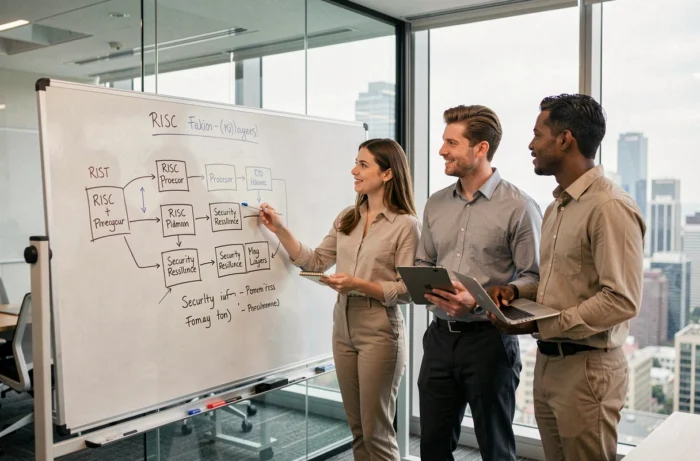
NIS 2 regulatory framework and RISC readiness in France
The European regulatory landscape is prompting organisations to formalise their approach to resilience. In France, ANSSI has made the Référentiel Cyber France (ReCyF) available as a tool to prepare for the NIS 2 Directive. According to Certi-Trust in November 2026, this framework remains a working document that may evolve before final adoption.
The legislative transposition of NIS 2 into French law has not yet been finalised. A resilience bill has been presented to the National Assembly, but its adoption timeline remains to be confirmed. For organisations preparing for these obligations, the RISC approach provides a structured framework: it inherently covers the risk management, data protection and vulnerability analysis requirements set out by NIS 2.
Gap between technical readiness and regulatory compliance
The challenge lies in the gap between an organisation’s technical maturity and the formal requirements of the future framework. A company may have effective detection tools without having documented its incident notification processes within the timeframes set by the Directive.
RISC helps bridge this gap by structuring incident response around four measurable phases: anticipation, resistance, recovery and adaptation. Each phase has verifiable indicators, making it easier to demonstrate compliance to regulatory authorities.
Current limitations and future directions for RISC
The RISC approach does not solve everything. Modelling dependencies between providers is hampered by a lack of transparency: most cloud providers do not publish details of their own subcontracting chains. Without this visibility, even a sophisticated trust model remains incomplete.
Integrating AI into defence mechanisms presents another challenge. Anomaly detection models generate false positives that overload security teams. Algorithmic frugality is becoming a measure of reliability, not just energy efficiency.
Collaboration between academic research and businesses’ operational needs is progressing, but slowly. LAAS-CNRS research into critical systems produces robust theoretical results, but transferring them into industrial tools takes several years. The gap between a laboratory prototype and a product ready for production deployment remains the main obstacle to widespread adoption of RISC as a resilience standard.


